One tenant could read every other tenant’s invoices
Trust, verified.
Full stack code, cloud, and runtime environments security audits using a proprietary AI toolset and industry-standard frameworks.
A maturity baseline the board could actually read
The mobile API that trusted the app too much
Every script on the payment page, accounted for
Ready for the auditor before the auditor arrived
A document portal that leaked through its filenames
Business logic that let a loan approve itself
A booking plugin that exposed the appointment book
OWASP Top 10:2025OWASP ASVS 5.0OWASP API Security Top 10OWASP WSTGNIST CSF 2.0NIST SP 800-115ISO/IEC 27001:2022SOC 2PCI DSS v4.0.1CIS Controls v8.1MITRE ATT&CKCVSS v4.0
Why we exist
Security work that tells you the truth, in words you can act on.
Most security reports are written to look thorough. Ours are written to be fixed. Penspy tests web applications and APIs by hand, the way a determined attacker would, and audits organisations against the frameworks their customers and auditors already use — OWASP, NIST CSF 2.0, ISO/IEC 27001:2022, SOC 2 and PCI DSS v4.0.1. Every finding comes with the request that proves it, the control it maps to, and a fix a developer can start on Monday. We do not inflate severities to look busy, we do not hand over a scanner export and call it a test, and we retest what you fix without charging you twice.
Every finding mapped to OWASP, NIST CSF 2.0, ISO 27001, SOC 2 or PCI DSS
Our team
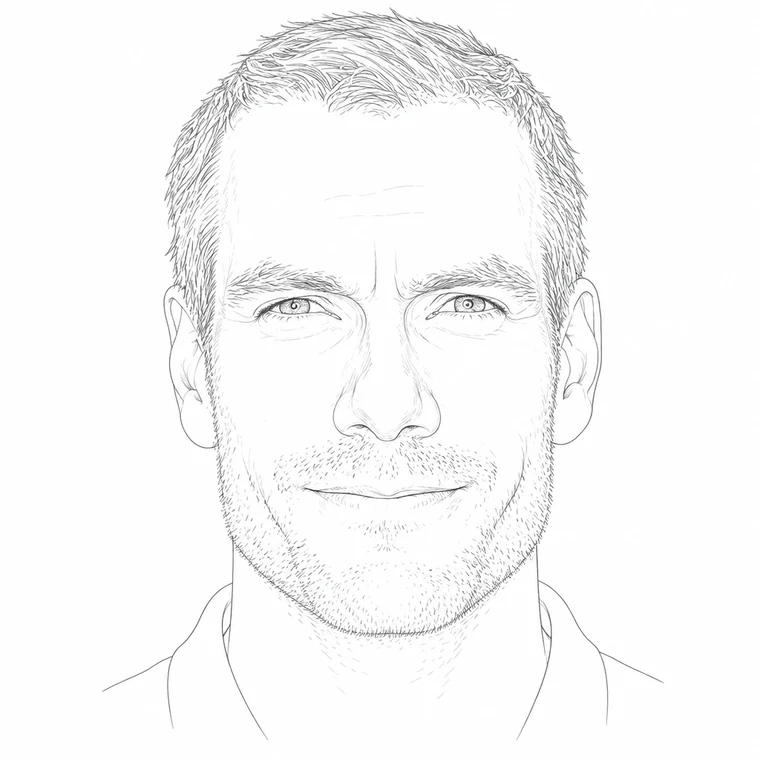
Jeff Haswell
Principal & Lead AssessorJeff has spent twenty years building web platforms and applications for businesses, which is exactly why he knows where they break: the permission check added in a hurry, the integration nobody revisited, the admin feature that shipped without a log. He leads every Penspy engagement, scopes it with you, maps the findings to the frameworks you answer to, and reviews every estimate and every report before it goes out.
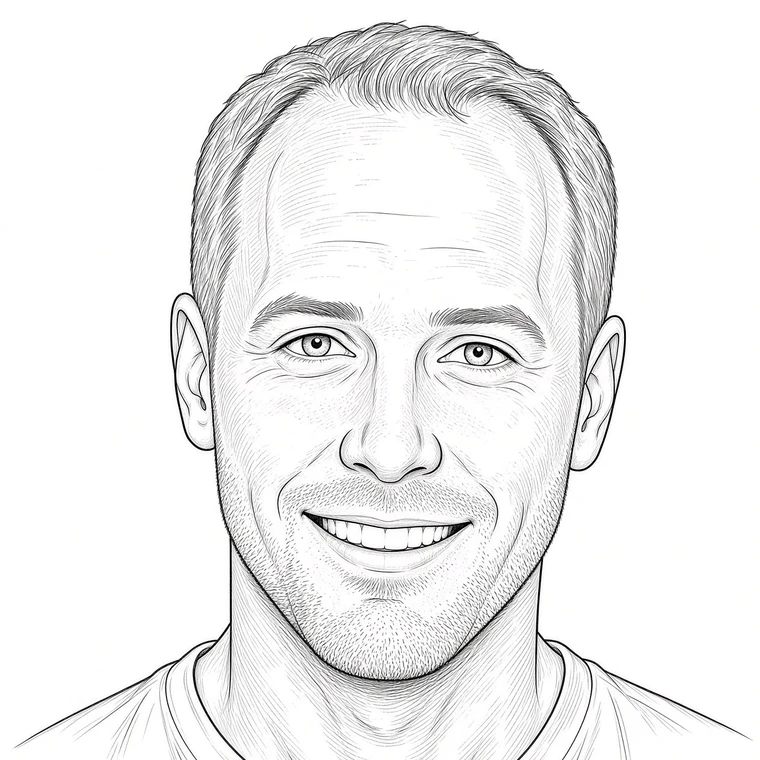
Grant Spencer
Offensive Security & InfrastructureGrant has twenty-five years of hardware and software development behind him, from embedded systems to the servers and networks businesses run on. He brings that depth to the technical side of every engagement — testing applications, APIs and the cloud and network infrastructure under them, reading code during reviews, and retesting each fix until it is verified closed rather than just reported.
// From the report
06 Findings
A finding should read like a fix, not a threat.
Representative excerpts, anonymised. Every finding ships with the request that reproduces it, the framework reference it maps to, a CVSS v4.0 score, and a fix your developers can act on.
Critical · CVSS 9.3
Changing the numeric ID inGET /api/v2/invoices/{id}returns invoices belonging to other tenants. Enforce ownership on the server for every object lookup, not only in the list view.
Broken object level authorisation
OWASP API1:2023 · ASVS V8
High · CVSS 8.2
Sending two transfer requests 40 ms apart lets both pass the daily-limit check. Take a row lock or use an atomic conditional update before the limit is evaluated.
Race condition in transfer limit
OWASP Top 10 A06 · WSTG-BUSL
High · CVSS 7.7
The “import from URL” field fetches internal addresses, including the cloud metadata service. Allow-list destinations and require IMDSv2 on every instance.
Server-side request forgery
OWASP Top 10 A01 · CWE-918
Medium · CVSS 5.3
Eleven third-party scripts load on the payment page, four of them through a tag manager with no integrity check. Inventory, justify and monitor each one.
Unmanaged payment-page scripts
PCI DSS v4.0.1 6.4.3 & 11.6.1
Medium · CVSS 6.1
Password reset tokens stay valid for 7 days and survive a password change. Expire them after one use and within 30 minutes.
Long-lived reset tokens
OWASP Top 10 A07 · ASVS V6
Low · informational
No issue found in the file-upload handler after 60 test cases. Recorded so you know it was tested, not skipped — a clean result is a result.
Upload handling: tested, holding
ASVS V5 · WSTG-BUSL-09
Know before they do.
Let’s Connect
or email hello@penspycyber.com
Questions
The ones we get asked most.
Straight answers on scope, cost, frameworks and what happens after the report. Anything missing, ask — a tester reads every message.
01What does Penspy Cyber Security actually do?
Two things that are usually sold by separate firms. We test web applications and APIs by hand to find what an attacker would find, and we audit organisations against recognised frameworks — NIST CSF 2.0, the CIS Controls, ISO/IEC 27001:2022 — and get them ready for SOC 2 and PCI DSS assessments. Every finding is mapped to the framework you already answer to.
02Who do you work with?
Teams who ship software and have to prove it is safe: SaaS companies facing enterprise security reviews, financial services and fintech, healthcare and health tech, e-commerce and retail, and professional-services firms holding client confidences. Browse representative engagements by sector from the menu.
03What is the difference between a vulnerability scan and a penetration test?
A scan is an automated tool checking for known weaknesses — fast, cheap, and blind to anything that needs context. A penetration test is a person working through your application the way an attacker would: chaining small issues together, abusing business logic, and checking whether one user can reach another user’s data. We use scanners as a starting point, never as the deliverable.
04How much does a penetration test or audit cost?
It depends on scope — how many roles, endpoints, environments or controls are involved. Rather than publish a number that fits nobody, the estimator on this site asks a few questions and gives you a range. Every estimate is reviewed by a lead assessor before a written proposal goes out.
05How long does an engagement take?
A typical web application test is one to three weeks of testing, with the draft report within five business days of the last test day. Framework audits usually run three to six weeks. Readiness programmes for SOC 2 or ISO 27001 run over two to four months, because they involve changing how things are done, not just writing it down.
06Which frameworks do you use?
Current editions, named precisely: the OWASP Top 10:2025, OWASP ASVS 5.0, the OWASP API Security Top 10 (2023) and the Web Security Testing Guide for applications; NIST CSF 2.0, the CIS Controls v8.1 and ISO/IEC 27001:2022 for organisations; SOC 2 and PCI DSS v4.0.1 for compliance; CVSS v4.0 for scoring. The approach page explains each one.
07Can you issue our SOC 2 report?
No, and nobody honest who is not a licensed CPA firm can. SOC 2 reports are attestation engagements issued by CPA firms under AICPA standards. What we do is the work before the auditor arrives — scoping the Trust Services Criteria, closing gaps, setting up evidence collection and running the penetration test most auditors expect to see — so the audit itself is uneventful.
08Will testing break our production application?
We agree the rules of engagement in writing before anything starts: what is in scope, testing windows, rate limits, which actions are off-limits and who to call if something looks wrong. We prefer a production-like staging environment, test production only where you want us to, and never run denial-of-service or destructive tests without explicit written approval.
09What do we get at the end?
A report with two audiences. An executive summary a board or customer can read, and a technical section where each finding has the steps and requests to reproduce it, a CVSS v4.0 score, the framework reference it maps to, and a recommended fix. After you remediate, we retest and issue a summary letter you can share with customers without exposing the detail.
10Is retesting included?
Yes. Retesting of every critical and high finding within 90 days of the report is included in every penetration test. A finding is closed when it is verified closed, not when the report is delivered.
11Who will we actually be working with?
Jeff Haswell scopes and leads every engagement and reviews every estimate and report before it goes out. Grant Spencer leads the technical testing — applications, APIs and the infrastructure under them — and the retests. Nobody is handed to an account manager, and the people who scope the work are the people who do it.
12Do you test APIs and mobile back ends?
Yes, and increasingly that is where the serious findings are. We test against the OWASP API Security Top 10, including the endpoints that exist but never made it into the documentation — mobile, partner and internal APIs are often less protected than the public one.
13What do you need from us before testing starts?
A signed authorisation and rules of engagement, test accounts for each role, the environment URL, and any API documentation or OpenAPI specs you have. For grey-box testing, a short walkthrough from a developer saves days of discovery. We send a checklist during scoping.
14Black box, grey box or white box — which should we choose?
For most web applications, grey box: we get credentials for each role and a walkthrough, which spends your budget on finding flaws rather than rediscovering what your team already knows. Black box simulates an outsider with nothing, and is usually less thorough per dollar. White box adds source code review, and suits teams who want the deepest assurance.
15How do you score severity?
With CVSS v4.0, adjusted for your environment, and explained in plain words. We do not inflate severities to make a report look busy, and we do not bury real issues as “informational”. If something is technically a finding but practically irrelevant to you, we say so.
16Can you help us get ready for ISO/IEC 27001:2022 certification?
Yes. We run a gap assessment against the standard’s clauses and its 93 Annex A controls, help you build the information security management system and the Statement of Applicability, and prepare you for the certification body’s audit. Certification itself is issued by an accredited certification body, not by us.
17What changed in PCI DSS v4.0.1 for online stores?
Several requirements that were best practice became mandatory on 31 March 2025. For e-commerce the two that matter most are 6.4.3, which requires an inventory, authorisation and integrity check for every script on a payment page, and 11.6.1, which requires detecting unauthorised changes to those pages. We test for both and help you put the controls in place.
18What is NIST CSF 2.0, and is it relevant to a smaller company?
It is the 2024 update of NIST’s Cybersecurity Framework, organised into six functions: Govern, Identify, Protect, Detect, Respond and Recover. Govern is new, and puts security ownership with leadership. It scales well to smaller organisations, which is why we use it to give leadership a one-page picture of where they stand.
19Do you offer ongoing testing rather than a once-a-year test?
Yes. Continuous testing covers each significant release or a fixed quarterly cadence, so new features are tested before your annual report goes stale. It suits teams shipping weekly, and is usually cheaper per test than separate engagements.
20Can you act as our security lead without a full-time hire?
Our fractional security lead service gives you a named senior person for a set number of hours each month: answering customer security questionnaires, owning the risk register, preparing for audits and advising engineering. It is how many companies get through their first SOC 2 before they hire a CISO.
21Do you do incident response?
We help you prepare for incidents — response plans, playbooks and tabletop exercises that rehearse a breach before it happens. For a live incident, we will help you triage and find the right forensic and legal support quickly, but we are not a 24/7 incident response retainer and will not pretend to be.
22How do you handle our data and findings?
As if they were the most sensitive thing we hold, because they are. Findings are stored encrypted, shared through an access-controlled portal rather than email attachments, and deleted on a schedule we agree. Test data we create is removed at the end of the engagement, and we sign your NDA as a matter of course.
23Do you only test, or do you help fix things too?
Both. Each report includes a specific remediation recommendation, and we are available to your developers while they fix — reviewing a proposed patch is faster and cheaper than discovering at retest that it missed a case.
24Where are you based, and do you work remotely?
We are based in Calgary, Alberta, and work with clients across Canada and the United States. Almost all testing is done remotely; on-site work is available for physical and internal network assessments.
25How do we get started?
Run the estimator for a range, or email hello@penspycyber.com and we will set up a scoping call. It helps to come with one thing: who is asking you for proof, and by when. That usually decides what kind of engagement you need.
10 / 25